Employees will start using new software long before IT ever knows it exists. Give them a simple prompt box, and they will start pasting customer data, spreadsheet figures, and internal notes into it just to finish their work faster.
You don’t need to ban every single application in sight. You just need to know what is running on your network, block what is dangerous, and keep sensitive company data where it belongs.
Managing AI security tools isn’t about buying a single piece of software off the shelf. It depends entirely on how your team uses artificial intelligence day to day.
- If you build AI models: You need code scans, infrastructure checks, and safeguards around model inputs and outputs.
- If you use existing GenAI tools: You need to see which tools employees visit, control what they paste into prompt boxes, and stop malicious inputs from hijacking responses.
Don’t confuse AI security tools with traditional cybersecurity. A threat-detection tool might use machine learning to catch malware on a laptop, but that same tool won’t notice when a manager pastes confidential medical records into a web chatbot. Standard Data Loss Prevention (DLP) tools catch basic file transfers, but they usually miss plain text prompts or hidden prompt manipulation entirely.
Before shopping around for vendors, answer one core question: Are you building custom AI models, or are your employees using third-party tools to get work done?
Three Big Risks You Need to Catch
1. Shadow AI
Shadow AI happens when employees sign up for unapproved apps using work or personal emails.
A copywriter opens a personal account to draft product copy. A finance manager drops a sales sheet into an unlisted online parser to clean up rows. Neither employee intends to cause damage, but IT remains blind to who owns the account and where that company data goes.
2. GenAI Data Leakage
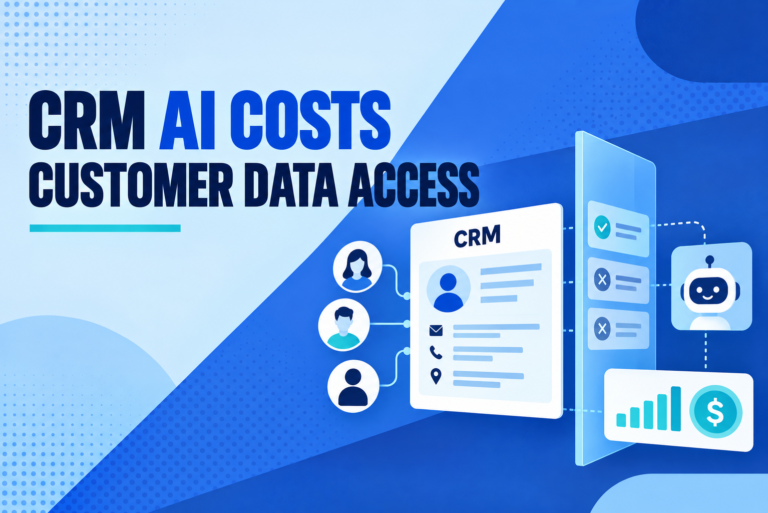
Data leaks start when someone pastes client details, payment records, or internal strategy notes into a prompt box.
Multi-page file uploads make this issue worse because employees rarely check every page before dragging a document into a browser. Approving an application isn’t enough. You have to decide what specific kinds of data are allowed into the prompt in the first place.
3. Prompt Injection
Prompt injection happens when malicious commands trick a language model into breaking its own safety rules.
- Direct Injection: A user types a command directly into the prompt box designed to bypass restrictions.
- Indirect Injection: Hidden instructions arrive inside external content,like a web page or PDF, that the model reads.
If your AI assistant reads a document containing hidden instructions, it might execute those commands without warning. Input filters help, but human approval on critical actions remains essential.
How to Evaluate an AI Security Tool
When reviewing tools with your team or managed IT provider, focus on practical tests over flashy feature lists:
- Visibility: Can the software identify individual users, or does it only track the IP address?
- Control Modes: Can you set rules to “alert only” while testing, and switch to “block” when an actual violation happens?
- Platform Integration: Does it fit into your current management console, or does it force your team to monitor another tab?
Deployment Framework and Operational Checklist
Evaluating software is only half the battle. Once you select your AI security tools, you need a realistic plan to run them without creating massive headaches for your IT team or slowing down daily operations.
A Simple Framework for Implementation
You don’t need a massive security team to handle this. You can adapt standard guidelines like the NIST AI Risk Management Framework 1.0 (NIST AI RMF) into four practical operational steps:
1. Govern
Draft a clear policy detailing which tools and data types are permitted. Employees should know exactly which services and accounts are approved, which information must stay out of prompts, and where to request an exception. A rule that simply says “use AI responsibly” leaves far too much room for confusion when someone is just trying to clear their inbox.
2. Map
Track which applications are actively running across all company devices. Discovery shouldn’t be about punishing employees; it’s about building an accurate inventory. You need to separate helpful, safe applications from unvetted sites that violate basic privacy standards.
3. Measure
Keep track of blocked attempts, policy flags, and potential data exposures. Running controls in “alert only” mode during your initial setup helps you see how people work without breaking their daily tasks. Once you understand the baseline, you can enforce hard blocks on high-risk actions.
4. Manage
Adjust your controls as new tools appear and staff workflows change. Assign a specific person on your team or at your Managed Service Provider (MSP) to review flags and handle access requests. Tools don’t run themselves—someone has to own the decisions.
Testing Tools in Real Work Conditions
Never buy an AI security tool based on a canned demo. Put candidate software through practical tests using synthetic data to see how it handles real work scenarios:
- Endpoint Coverage: Test the software across both Windows and macOS devices using your team’s primary web browsers. Verify if protection works when employees log in from remote locations or unmanaged networks.
- Contextual Inspection: Check how the tool handles typed prompts, copy-pasted text blocks, and file uploads. A tool that stops a user from pasting a spreadsheet might completely miss that same data hidden inside a PDF attachment.
- User Experience: Observe what the employee sees when an action gets blocked. Does the software show a clear, helpful message explaining why the prompt was stopped, or does it just crash the browser tab?
Setting Operational Responsibilities
Whether you manage security internally or work with an MSP, establish clear responsibilities from day one:
- Policy Updates: Decide who updates the list of blocked and allowed applications as new tools pop up every week.
- Alert Triage: Define who reviews flagged events daily so real risks don’t get lost in a sea of harmless notifications.
- Exception Handling: Create a fast track for employees to request approval for new tools needed for urgent projects.
Good security doesn’t mean stopping your team from using modern tools. By pairing clear rules with practical controls, you can let your employees use AI to work faster while keeping your critical business data completely safe.